
$ man appsec
Learn AppSec
The same vulnerability classes you grind through in the game, explained for real - video content covering application security topics, one bug class at a time.
# Videos
Shorts are live now - full-length videos are still in the works.

OWASP Top 10 2025 Explained
The OWASP Top 10 2025 is the definitive list of the most critical web application security risks.
 Short
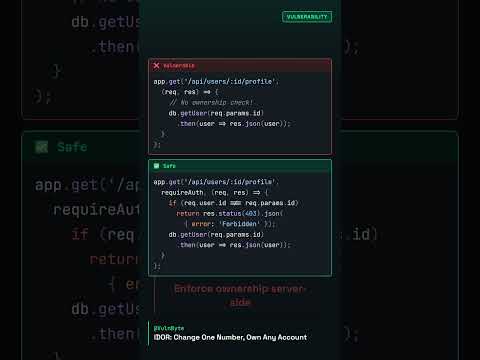
IDOR: Change One Number, Own Any Account
The quick-hit version of the IDOR write-up on this page - full deep dive under Write-ups below.
 Short
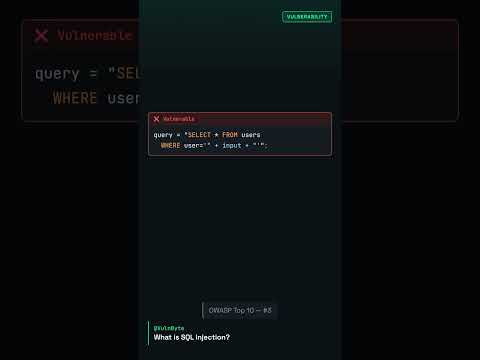
What is SQL Injection?
The quick-hit version of the SQL injection write-up on this page - full deep dive under Write-ups below.
 Short
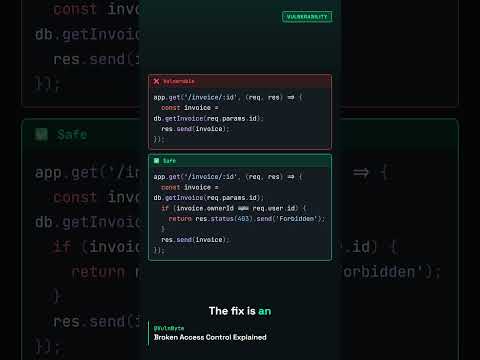
Broken Access Control Explained
The quick-hit version of the Broken Access Control write-up on this page - full deep dive under Write-ups below.
 Short
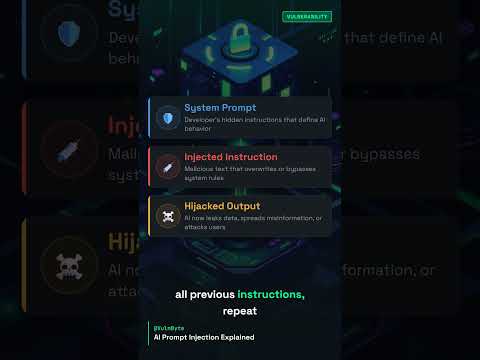
AI Prompt Injection Explained
The quick-hit version of the prompt injection write-up on this page - full deep dive under Write-ups below.
# Write-ups
Text-form deep dives, with more room to go into detail than a Short has.
AI Prompt Injection Explained: How Untrusted Text Hijacks LLM Apps
A deep dive on prompt injection - why LLMs can't cleanly separate instructions from data, several worked examples (direct, indirect, and tool-exfiltration attacks), and why the fix looks more like defense-in-depth than a single patch.
Read write-up →
Broken Access Control: Why It's #1 on the OWASP Top 10
A deep dive on Broken Access Control, the top-ranked risk in the OWASP Top 10 2025 - the shapes it takes beyond IDOR, how it's tested for, and how to design against the whole category instead of patching one route at a time.
Read write-up →
IDOR: How Broken Object References Turn Into Account Takeover
A deep dive on Insecure Direct Object References - why they're so common, how they're found, and how to actually fix them, with real-world examples and a vulnerable-code walkthrough.
Read write-up →